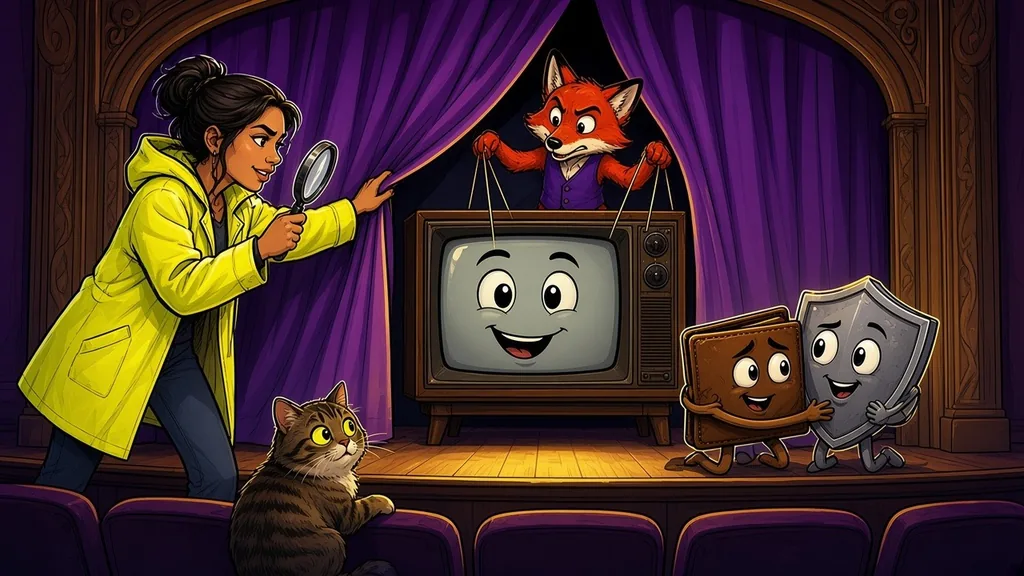
The FBI says a scam it calls FaceStealer stole more than $400 million in crypto over 18 months. It did not rely on fake websites or cold messages from strangers. It used video calls that looked like they came from people the victims already knew.
The week of November 9, 2026, the Justice Department announced it had seized the cloud servers behind the scheme along with more than 900 secretly recorded webcam videos of past victims. The scheme is down for now. The playbook is not. Here is how FaceStealer works, why it fooled careful people and the simple habits that would have stopped it.
What is the FaceStealer crypto scam?
FaceStealer is the FBI's name for a social engineering scheme run by North Korean hackers. The Justice Department ties it to the group known as BlueNoroff, Sapphire Sleet and APT38. It targets people who work in crypto and in open-source software, plus anyone with money or access worth stealing.
The goal is simple. Get you onto a fake Zoom or Teams call, make you trust what you see and get you to install malware yourself. Once your computer is infected the attackers can drain wallets, steal logins and take over your messaging accounts. In some cases the DOJ says they waited months or more than a year after the first break-in before stealing funds.
The same announcement covered a court-approved seizure of more than $1.2 billion stolen in the record Binance hack. We explain what an exchange hack means for regular customers in what happens if a crypto exchange gets hacked.
How the scam works step by step
The FBI lays out the lifecycle in five stages. Security researchers at JUMPSEC and Arctic Wolf filled in the details, as The Hacker News reported.
- They hijack someone you know. An earlier victim's Telegram, LinkedIn, Slack or Discord account is taken over. Their contacts and chat history are now in the attackers' hands.
- They message you as that person. The pitch is usually business, such as an investment idea or a partnership. It reads like your contact because it is their account.
- They send a meeting link. Often a scheduling invite first, then a link shortly before the call. The link points to a lookalike domain dressed up as Zoom or Teams.
- They fill the room with fake faces. You see a prerecorded webcam video of your contact and sometimes other "participants." Some are AI deepfakes of known people in the industry built from interviews and conference talks.
- They break the call on purpose. A message says they cannot hear you or that your app needs an update. The "fix" is a link, installer or command to paste into your terminal. That is the malware.
Then the cycle repeats. Your webcam was recorded during the call. Your accounts become the next lure for your own contacts.
Why careful people fell for it
FaceStealer beat the advice most of us were taught. "Only trust people you know" did not help because the message really came from a known account. "Check if it is a real person on video" did not help because the video really was that person, just recorded earlier.
The attackers also aimed high. Arctic Wolf found that over 80% of more recent targets were founders and executives across 58 countries. These are people with signing keys, exchange access and large balances.
AI made it cheaper to scale. The researchers say the group used generative AI tools to make avatars, artwork and synthetic participant videos. The FBI's 2025 Internet Crime Report already showed more than $11 billion in reported crypto-related losses in a single year, and Decrypt counted over 22,000 AI-linked complaints. Fake video calls are the next step in that trend.
FaceStealer red flags and what to do instead
| Red flag | Why it matters | Safe move |
|---|---|---|
| A known contact suddenly pitches a deal or call | Their account may be hijacked | Confirm with them on a different channel you already use |
| Meeting link with an odd domain | Real Zoom and Teams links use official domains | Open the app yourself and join by meeting ID |
| You wait alone, then get a "can't hear you" message | The error is staged | Leave the call and rejoin through the official app |
| A prompt to install an SDK, extension or update mid-call | This is the malware drop | Never install anything during a call |
| A request to paste a command into Terminal or Run | A ClickFix-style trick | No real meeting app asks you to do this |
| A request to share your screen or give remote control | They can watch or steer your device | Decline. No real business needs it |
| Talk of wallets, seed phrases or moving funds | The end goal is your crypto | Stop. Your recovery phrase is never shared |
A 10-step checklist to protect your crypto
- Verify every unexpected invite on a second channel. Call or text the person on a number you already had.
- Join meetings only from the official app or a link you typed yourself.
- Treat any in-call "fix" as an attack. Update apps only from the app store or the vendor's own site when no call is running.
- Never paste commands you do not understand into a terminal, Run box or browser bar.
- Keep your seed phrase offline and never type it into a computer. Our guide on how to keep crypto safe walks through setup.
- Use a hardware wallet for long-term holdings so malware on your laptop cannot sign transactions alone.
- Take calls on a device that does not hold your wallets if you take many business calls.
- Turn on app-based or hardware-key two-factor authentication on email, exchange and messaging accounts.
- Agree on a code word with family and business partners for money talk.
- Report it fast. File with the FBI at IC3.gov and warn your contacts if your account was taken over.
If you want a simple safety-first plan before you invest more, our free CCF Quick Start Guide lays out the basics in plain steps.
What to do if you clicked the fix
Act in minutes, not days.
- Disconnect the computer from the internet and stop using it for anything financial.
- From a clean device, move funds to a brand new wallet created on a device you trust. The old seed phrase should be treated as burned.
- Change passwords and log out other sessions on email, exchanges and messaging apps from that clean device.
- Warn your contacts that messages from you may be fake.
- Report to IC3 and to any exchange you use. Keep notes and screenshots.
- Have the infected machine wiped before you use it again.
Moving fast matters because the DOJ says these hackers often lurk quietly before they strike. For more patterns to watch, see our list of crypto scams to avoid and how to check if a crypto website is legit.
How AI can help you stay safe
AI is not only a tool for attackers. Before you click an invite, paste the link and message into an AI assistant and ask it to check the domain and list red flags. Ask it to explain any command before you would ever run one. Then verify the answer yourself. The final check is always a second channel to the real person.
The bottom line on FaceStealer
FaceStealer worked because it borrowed trust. A real account, a familiar face and a believable glitch did the rest. The servers are seized but the method will return under new names. Build one reflex: if a call asks you to install, run or paste anything, hang up and verify.
CCF teaches digital assets, from Bitcoin and crypto to tokenized stocks and beyond, with AI as your research partner and security built in from day one. If you want structured help, explore our CCF programs.
Frequently asked questions
What is FaceStealer?
FaceStealer is the FBI's name for a North Korean scheme that uses fake Zoom and Teams calls, recorded webcam video and deepfakes to trick crypto holders into installing malware. It stole more than $400 million over 18 months.
How much money did FaceStealer steal?
The FBI says more than $400 million in crypto over the 18 months before the November 2026 disruption.
Is the FaceStealer scam over?
The FBI seized the cloud servers and more than 900 victim videos. The group behind it is still active and similar fake meeting tricks keep appearing, so stay alert.
How do I know if a Zoom link is fake?
Check the domain before you click. Safer still, open the official Zoom or Teams app and join with the meeting ID. Be suspicious of any link that asks you to download something to join.
Can a deepfake really look like someone I know?
Yes. In FaceStealer many faces were real recordings of earlier victims, and some were AI deepfakes built from public videos. Seeing a familiar face is not proof you are talking to that person.
What should I do if I installed a fake Zoom update?
Disconnect the device, move your crypto to a new wallet from a clean device, change passwords, warn your contacts and report it to IC3.gov.
Does a hardware wallet protect me from FaceStealer?
It helps a lot because malware cannot sign transactions without the device and your approval. It does not protect a seed phrase you typed into an infected computer, and it cannot protect funds left on an exchange account the attackers log into.
Who does FaceStealer target?
Mainly people in crypto, open-source software and finance, especially founders and executives. Anyone holding crypto can be reached through a hijacked contact.
This article is general education, not financial, legal or security advice. Facts are current as of November 15, 2026, and details may change as investigations continue. Trading and investing in digital assets involves risk including loss of your capital.
Free Quick Start Guide
Want more like this?
Get the free CCF Quick Start Guide. Security and first-buy checklists, chart basics, the 1% risk rule and paper trading in one 42-page PDF.
Education only, not financial advice. We never share your details.
Prefer to talk? Book a call
Written by
CCF · Co-founder
Joshua Montoya is a bestselling author and speaker and an equal co-founder of CCF with Marty Cooney. His story is from fast food to freedom: he left fast food for a digital marketing career in 2010 and has been in crypto since 2017. His mission is the power of 1% and he teaches everyday people to buy, sell, trade and secure digital assets with risk management and independent decisions first.
CCF · Co-founder
Marty Cooney is a bestselling author and speaker and an equal co-founder of CCF with Joshua Montoya. His story is from digital publishing to digital assets: he built a career in online marketing and publishing and has been in crypto since 2017. His motto is show up daily and stack your 1% and he teaches everyday people to buy, sell, trade and secure digital assets with a clear process first.
Educational content only. This article is general education about digital assets, trading and investing. It is not individualized financial, investment, legal or tax advice, and it is not a recommendation to buy or sell any asset. Crypto markets are volatile and involve risk, including loss of principal; leveraged products can lose more than the amount committed. CCF does not guarantee any outcome or return. Do your own research and consider speaking with a licensed professional about your situation.